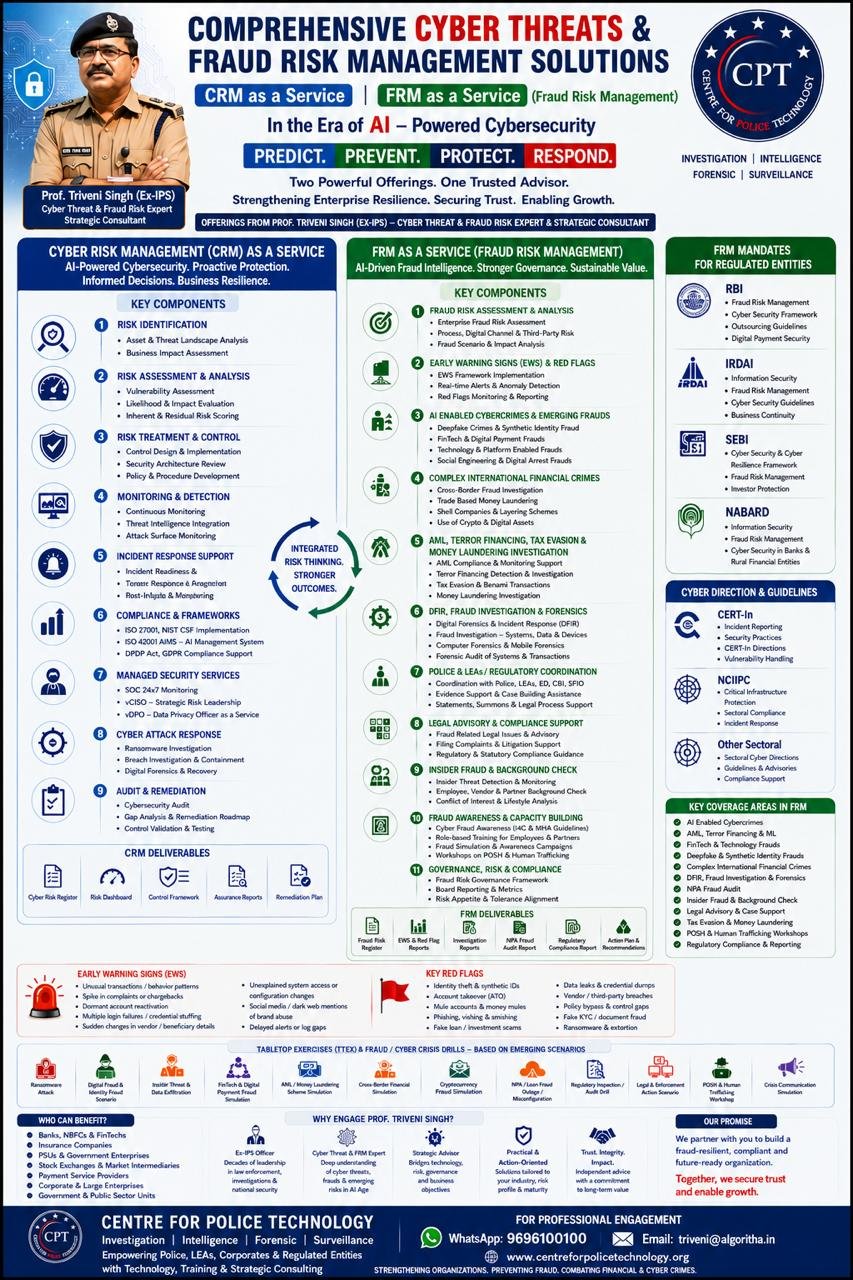
As cyber threats, AI-enabled crimes, financial frauds, regulatory obligations and complex technology risks converge, corporates, BFSI institutions, FinTechs, PSUs and other regulated entities increasingly require an integrated approach to Cyber Risk Management (CRM) and Fraud Risk Management (FRM).
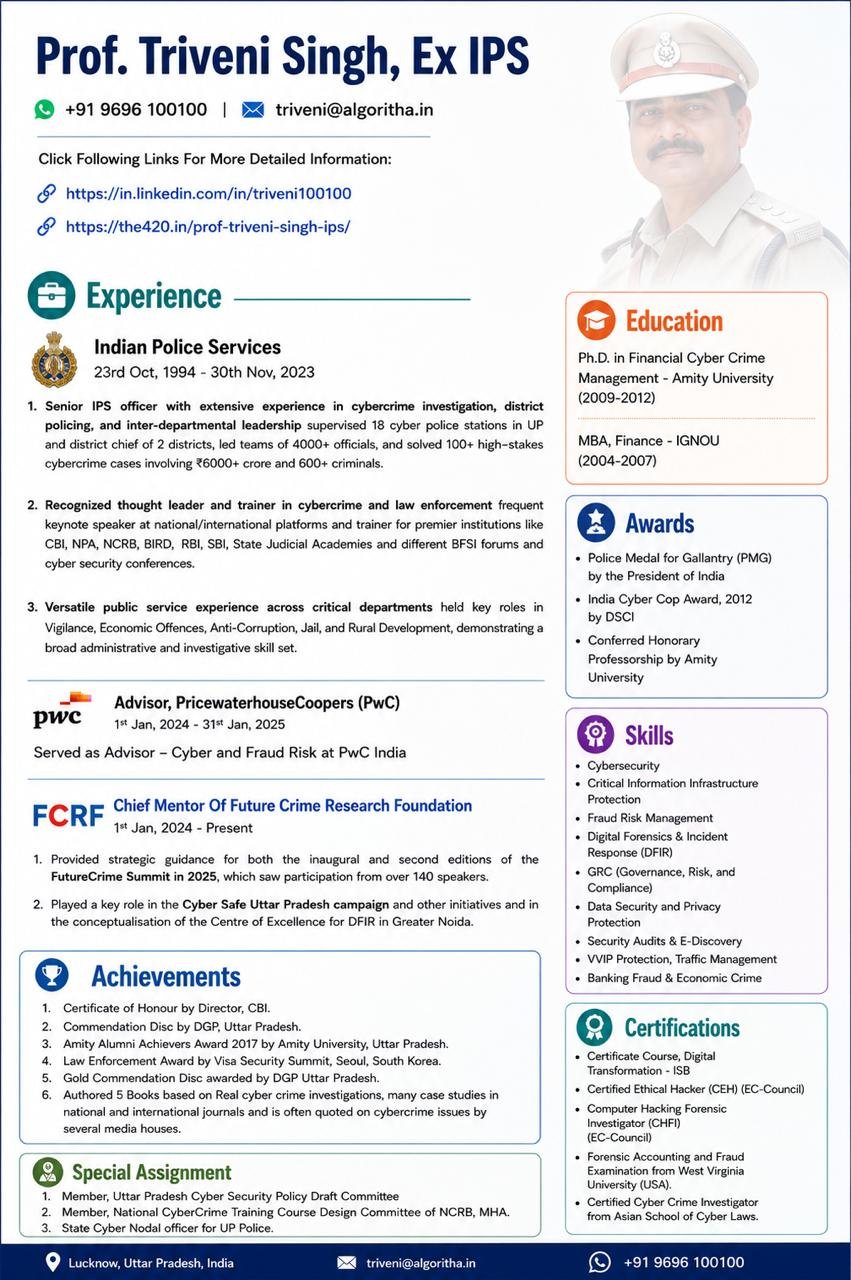
Prof. Triveni Singh (Ex-IPS), Cyber Threat & Fraud Risk Expert and Strategic Consultant, is offering CRM as a Service and FRM as a Service for organisations seeking specialised advisory, investigation, compliance, cyber resilience, fraud prevention and capacity-building support.
The proposition brings together two powerful offerings under one trusted advisor, with the objective of strengthening enterprise resilience, securing trust and enabling sustainable growth.
Cyber Risk Management (CRM) as a Service
The CRM offering focuses on AI-powered cybersecurity, proactive protection, informed decisions and business resilience.
1. Risk Identification
The engagement begins with asset and threat landscape analysis and business impact assessment, enabling organisations to understand critical assets, emerging threats and potential consequences to business operations.
2. Risk Assessment & Analysis
Services include vulnerability assessment, likelihood and impact evaluation, and inherent and residual risk scoring, helping management prioritise risks according to their potential business impact.
3. Risk Treatment & Control
The offering covers control design and implementation, security architecture review, and policy and procedure development, providing a structured approach to reducing identified cyber risks.
4. Monitoring & Detection
Organisations can strengthen their security posture through continuous monitoring, threat intelligence integration and attack surface monitoring.
5. Incident Response Support
The service includes incident readiness and playbooks, response guidance, and post-incident review and learning, helping organisations prepare for and respond effectively to cyber incidents.
6. Compliance & Frameworks
The CRM offering assists organisations with implementation and compliance relating to:
- ISO 27001
- NIST Cybersecurity Framework
- ISO 42001 AIMS – AI Management System
- DPDP Act compliance
- GDPR compliance
This enables organisations to integrate cybersecurity, privacy and responsible AI governance into their enterprise risk framework.
7. Managed Security Services
Specialised managed and fractional leadership support includes:
- SOC 24×7 Monitoring: Continuous monitoring and detection capability for cyber threats and suspicious activities.
- vCISO – Strategic Risk Leadership: Virtual Chief Information Security Officer support for organisations requiring senior cybersecurity leadership without maintaining a full-time CISO structure.
- vDPO – Data Privacy Officer as a Service: Professional privacy leadership and advisory support for data protection and privacy compliance.
8. Cyber Attack Response
Specialised support is available for:
- Ransomware investigation
- Breach investigation and containment
- Digital forensics and recovery
The objective is not merely to respond to an attack but to understand its origin, impact and modus operandi, preserve evidence, support recovery and reduce the probability of recurrence.
9. Audit & Remediation
The offering further includes:
- Cybersecurity Audit
- Gap Analysis & Remediation Roadmap
- Control Validation & Testing
- CRM Deliverables
Depending upon the scope of engagement, deliverables can include a Cyber Risk Register, Risk Dashboard, Control Framework, Assurance Reports and Remediation Plan.
The overall philosophy is based on integrated risk thinking for stronger outcomes.
FRM as a Service — Fraud Risk Management
The FRM offering provides AI-driven fraud intelligence, stronger governance and sustainable value, with a particular focus on emerging technology-enabled frauds and complex investigations.
1. Fraud Risk Assessment & Analysis
The service covers enterprise fraud risk assessment, process, digital channel and third-party risk assessment, and fraud scenario and impact analysis.
It helps organisations identify where fraud can originate, how vulnerabilities may be exploited and what financial, regulatory, reputational and operational consequences could follow.
2. Early Warning Signs (EWS) & Red Flags
The FRM programme supports EWS framework implementation, real-time alerts and anomaly detection, and red-flag monitoring and reporting.
Important Early Warning Signs can include:
- Unusual transactions or behaviour patterns
- Spike in complaints or chargebacks
- Dormant account reactivation
- Multiple login failures or credential stuffing
- Sudden changes in vendor or beneficiary details
- Unexplained system access or configuration changes
- Social media or dark-web mentions of brand abuse
- Delayed alerts or log gaps
Important fraud red flags include:
- Identity theft and synthetic identities
- Account takeover (ATO)
- Mule accounts and money mules
- Phishing, vishing and smishing
- Fake loan and investment scams
- Data leaks and credential dumps
- Vendor or third-party breaches
- Policy bypass and control gaps
- Fake KYC and document fraud
- Ransomware and extortion
3. AI-Enabled Cybercrimes & Emerging Frauds
A major focus of the offering is the new generation of technology-enabled crime, including:
- Deepfake crimes and synthetic identity fraud
- FinTech and digital payment frauds
- Technology and platform-enabled frauds
- Social engineering and digital arrest frauds
As artificial intelligence changes both legitimate business and criminal ecosystems, organisations require fraud controls capable of addressing AI-generated identities, manipulated content, automated social engineering and increasingly sophisticated digital deception.
4. Complex International Financial Crimes
Specialised advisory and investigation support is offered for complex financial crimes involving:
- Cross-border fraud investigation
- Trade-based money laundering
- Shell companies and layering schemes
- Use of crypto and digital assets
Such cases frequently require understanding financial transactions, corporate structures, digital evidence, international linkages and multiple layers of beneficiaries and intermediaries.
5. AML, Terror Financing, Tax Evasion & Money Laundering Investigation
The offering includes professional support relating to:
* AML compliance and monitoring
* Terror financing detection and investigation
* Tax evasion and Benami transactions
* Money laundering investigation
This capability is particularly relevant for organisations facing increasingly complex financial transactions and regulatory scrutiny.
6. DFIR, Fraud Investigation & Forensics
Specialised investigative and forensic capabilities include:
* Digital Forensics & Incident Response (DFIR)
* Fraud investigation involving systems, data and devices
* Computer forensics and mobile forensics
* Forensic audit of systems and transactions
The service combines investigative understanding with digital and financial evidence analysis, helping organisations establish what happened, how it happened, who may have been involved and what evidence is available.
7. Police / LEAs / Regulatory Coordination
One of the distinctive aspects of the offering is support in dealing with Police, Law Enforcement Agencies and regulatory authorities.
This can include coordination and professional assistance involving Police, ED, CBI and SFIO, along with:
* Evidence support and case-building assistance
* Statements
* Summons
* Legal process support
Prof. Singh’s policing and cybercrime investigation experience provides organisations with an understanding of how corporate incidents may transition into criminal investigations, regulatory proceedings and evidentiary processes.
8. Legal Advisory & Compliance Support
The offering includes support concerning:
* Fraud-related legal issues and advisory
* Filing complaints and litigation support
* Regulatory and statutory compliance guidance
This helps bridge the often-complex gap between technical incidents, fraud investigations, evidence and subsequent legal or regulatory action.
9. Insider Fraud & Background Check
Insider risk is an important component of modern fraud risk management.
The service covers:
* Insider threat detection and monitoring
* Employee, vendor and partner background checks
* Conflict-of-interest and lifestyle analysis
The objective is to help organisations identify potential internal vulnerabilities while strengthening integrity and due-diligence processes.
10. Fraud Awareness & Capacity Building
A strong fraud risk programme also depends upon people. The offering therefore provides:
* Cyber Fraud Awareness based on I4C & MHA guidelines
* Role-based training for employees and partners
* Fraud simulation and awareness campaigns
* Workshops on POSH and Human Trafficking
These programmes can be customised for boards, senior executives, security teams, compliance professionals, investigators and employees.
11. Governance, Risk & Compliance
The FRM engagement can further support organisations through:
* Fraud Risk Governance Framework
* Board Reporting & Metrics
* Risk Appetite & Tolerance Alignment
FRM Deliverables
Depending upon organisational requirements, deliverables can include:
Fraud Risk Register | EWS & Red Flag Reports | Investigation Reports | NPA Fraud Audit Report | Regulatory Compliance Report | Action Plan & Recommendations
NPA Fraud Audit
For banks and financial institutions, the FRM portfolio includes NPA Fraud Audit, supporting the examination of potentially fraudulent conduct associated with stressed and non-performing accounts.
This capability complements forensic audit, transaction analysis, red-flag identification, investigation and regulatory reporting.
FRM Mandates for Regulated Entities
The offering recognises that fraud risk management cannot operate independently of regulatory expectations.
RBI
Coverage can include requirements and expectations relating to:
* Fraud Risk Management
* Cyber Security Framework
* Outsourcing Guidelines
* Digital Payment Security
IRDAI
Relevant areas include:
* Information Security
* Fraud Risk Management
* Cyber Security Guidelines
* Business Continuity
SEBI
Support can address areas relating to:
* Cyber Security & Cyber Resilience Framework
* Fraud Risk Management
* Investor Protection
NABARD
Relevant requirements can include:
* Information Security
* Fraud Risk Management
* Cyber Security requirements for Banks and Rural Financial Entities
Cyber Directions & Guidelines
The integrated CRM-FRM model also takes account of important national and sectoral cybersecurity requirements.
CERT-In
The engagement can support organisations concerning incident reporting, security practices, CERT-In directions and vulnerability handling.
NCIIPC
For organisations connected with critical infrastructure, relevant areas include Critical Infrastructure Protection, sectoral compliance and incident response.
Other Sectoral Directions
The advisory model can also incorporate applicable sectoral cyber directions, guidelines, advisories and compliance requirements.
Tabletop Exercises & Fraud/Cyber Crisis Drills
Organisations can conduct customised Tabletop Exercises (TTEx) and Fraud/Cyber Crisis Drills based on emerging scenarios.
Scenarios can include:
Ransomware Attack | Digital Fraud & Identity Fraud | Insider Threat & Data Exfiltration | FinTech & Digital Payment Fraud | AML/Money Laundering Scheme | Cross-Border Financial Crime | Cryptocurrency Fraud | NPA/Loan Fraud | Regulatory Inspection/Audit | Legal & Enforcement Action | POSH & Human Trafficking Workshop | Crisis Communication Simulation
Such exercises enable boards, management teams and operational stakeholders to test their preparedness before facing an actual crisis.
Who Can Benefit?
The integrated CRM and FRM offerings are designed for a broad range of organisations, including:
* Banks, NBFCs and FinTechs
* Insurance Companies
* PSUs and Government Enterprises
* Stock Exchanges and Market Intermediaries
* Payment Service Providers
* Corporates and Large Enterprises
* Government and Public Sector Units
Why Engage Prof. Triveni Singh?
- As an Ex-IPS Officer, Prof. Triveni Singh brings decades of leadership experience in law enforcement, investigations and national security.
- As a Cyber Threat & FRM Expert, his work combines an understanding of cyber threats, frauds and emerging risks in the AI age.
- As a Strategic Advisor, he bridges technology, risk, governance and business objectives, helping organisations approach cyber and fraud risk as enterprise-level challenges rather than isolated technical issues.
The engagement is intended to remain practical and action-oriented, with solutions tailored to an organisation’s industry, risk profile and maturity.
The underlying professional values are Trust. Integrity. Impact. The objective is to provide independent advice with a commitment to long-term value.
Building Fraud-Resilient and Cyber-Resilient Organisations
Cybersecurity and fraud risk are increasingly interconnected. A ransomware incident may become a forensic investigation; a deepfake may enable financial fraud; an insider may facilitate data theft; a FinTech vulnerability may trigger a regulatory investigation; and a cross-border transaction may involve cybercrime, money laundering, cryptocurrency and multiple law-enforcement jurisdictions.
The integrated CRM as a Service + FRM as a Service model is therefore designed to help organisations Predict. Prevent. Protect. Respond.
The promise is straightforward:
We partner with you to build a fraud-resilient, compliant and future-ready organisation.
Together, we secure trust and enable growth.
⸻
Centre for Police Technology
Investigation | Intelligence | Forensic | Surveillance
Empowering Police, LEAs, Corporates and Regulated Entities with Technology, Training & Strategic Consulting.
For Professional Engagement
Prof. Triveni Singh (Ex-IPS)
Cyber Threat & Fraud Risk Expert | Strategic Consultant
WhatsApp: 9696100100
Email: triveni@algoritha.in
Centre for Police Technology
Strengthening Organisations. Preventing Fraud. Combating Financial & Cyber Crimes.